
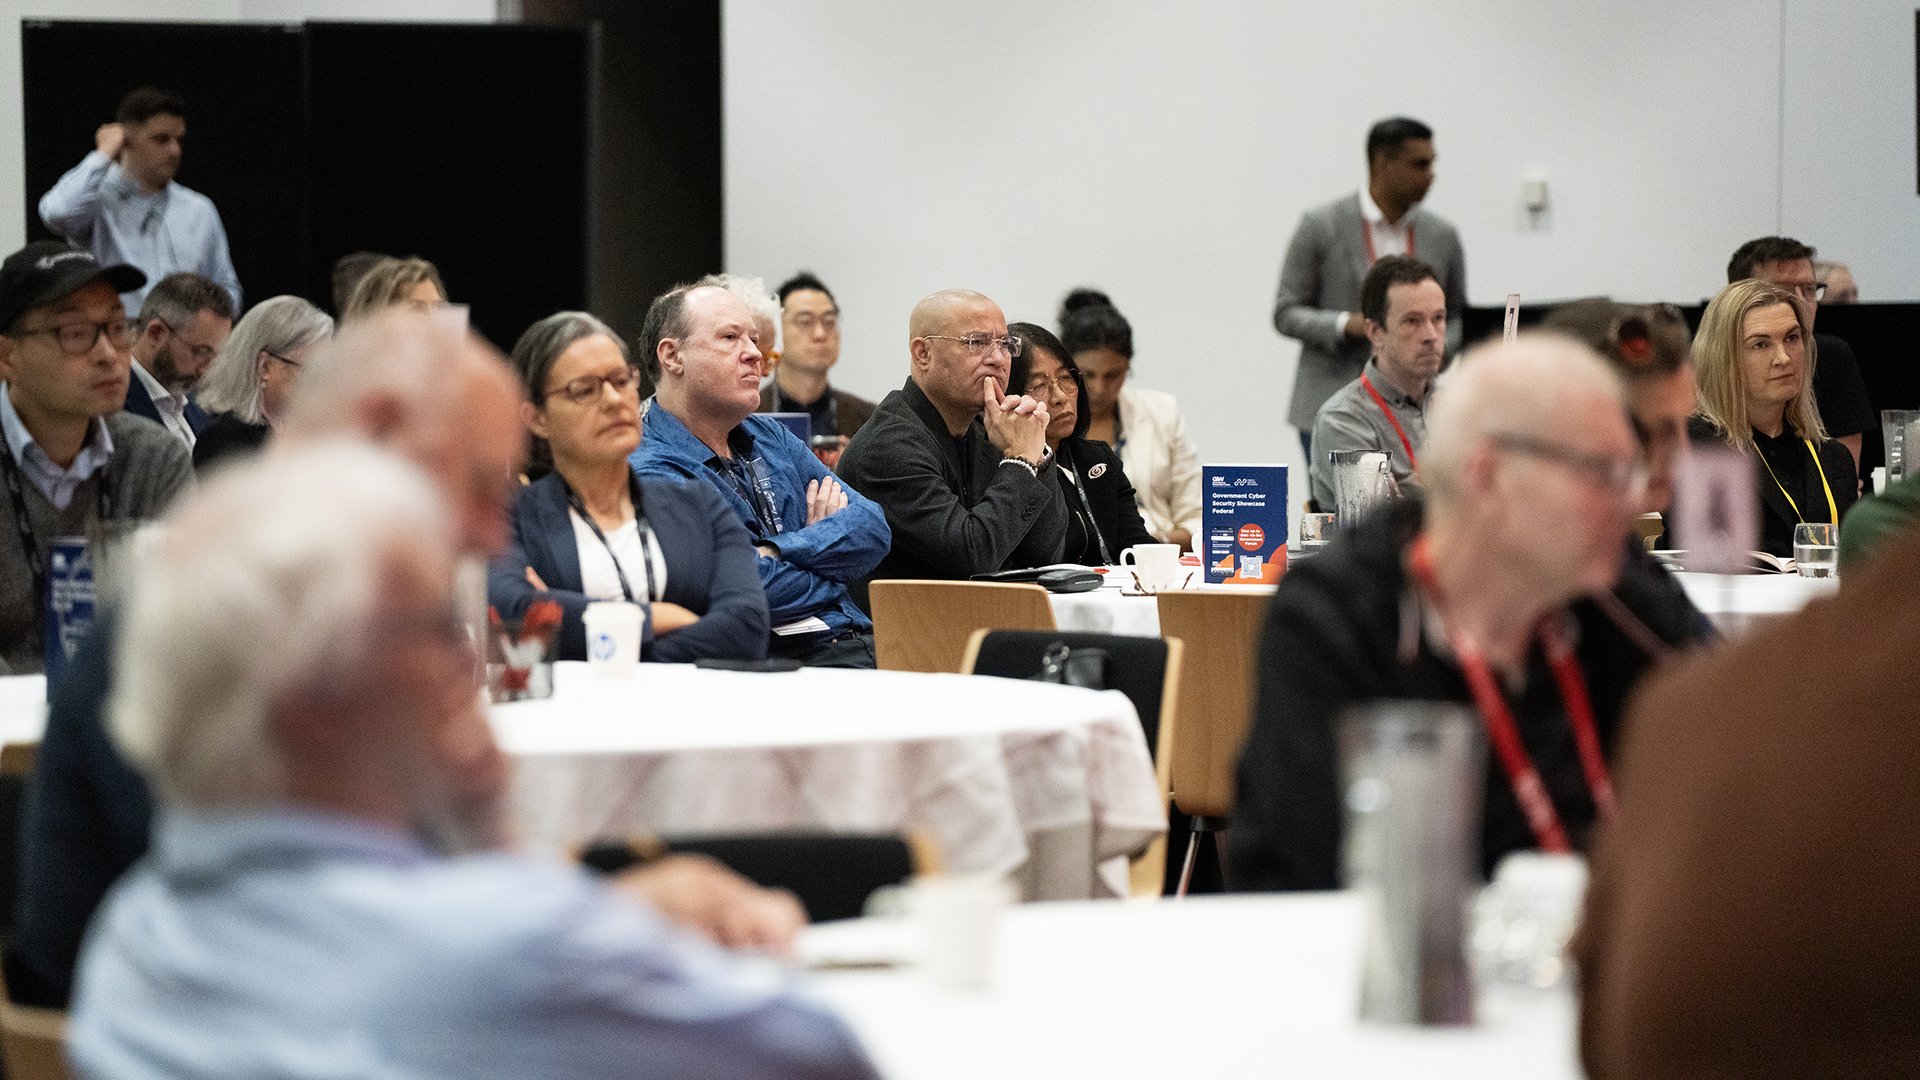
Chair Opening: Government Spending, Direction and Priorities
Angelo Friggieri — CyberCX
- Government cyber investment should protect essential services from disruption and sabotage, not focus only on data theft.
- Artificial intelligence (AI) can increase the speed and scale of attacks. Security teams should assess how to use it defensively while keeping people accountable.
- Apply identity and access controls to AI agents, and keep testing the basics, including network segmentation, passwords and monitoring coverage.
Deciphering AI Identity Security Gateways
Timothy Wedande — Saviynt
- AI agents can carry out chains of actions across systems. Treat their identities, permissions and human ownership as part of access management.
- Content filtering, routing and identity controls address different risks. Assess gaps across the layers rather than assuming one gateway covers every need.
- Test whether agent actions match their intended purpose, enforce separation of duties and investigate anomalies. Check performance and false positives in your own environment.
Faster Than the Threat: How AI Turns Intelligence into Action You Can Trust
Naran McClung — Macquarie Government
- Automated triage and threat hunting can help security teams handle large volumes of alerts, but the underlying threat intelligence needs to be checked across reliable sources.
- Treat AI-generated findings as hypotheses and test them against security telemetry. Escalate unfamiliar or novel cases to a human analyst.
- Test models and workflows in stages before production. Track decisions, protect sensitive information and give staff time to refine the tools.
Chair Opening
Nick Klein — SANS Institute
- A technical fix is not enough if the organisation does not address why a weakness persisted. Investigate the decisions, workload and processes behind recurring gaps.
- Treat supplier security as part of your own security. Check contractual obligations, everyday access practices, monitoring and incident escalation.
- Give security teams time, technical training and opportunities to test defences. These foundations remain important as AI accelerates attacks.
Building Trust in AI Through Better Data Governance
Matt Patterson — Proofpoint
- AI tools can expose data that was already over-shared. Find sensitive information, review permissions and involve data owners in fixing inappropriate access.
- Map both approved and unapproved AI use, including features embedded in existing software. Understand what information users and agents send to each tool.
- Monitor data movement and apply proportionate controls, such as blocking or redacting sensitive content. Distinguish malicious behaviour from mistakes or compromised accounts when responding.
Can Government Move Faster Without Weakening Trust?
Sajid Hassan — Australian National University
Dimitar Dimitrovski — Fair Work Ombudsman
Chris Zhang — National Measurement Institute
George Hlaing — National Consulting Partners
Craig Magee — Splunk
Nick Klein, moderator — SANS Institute
- Start with the service problem and the outcome for citizens. AI may help with low-judgement tasks, but a person must remain accountable for government decisions.
- Review AI features embedded in suppliers’ products and map where data moves. New capabilities can add risk even when an agency has not deliberately selected them.
- Consider how citizens may use AI agents to contact government. Authentication, accessibility and fraud controls need to account for those interactions without assuming every agent is malicious.
Australia’s Critical Infrastructure Is Now a Cyber Battleground
Savithri Munasinghe — Commonwealth Superannuation Corporation
Karen Schilling — Canberra Cyber Hub
Peter Baussmann — Airlock Digital
Nick Klein, moderator — SANS Institute
- Compliance is a starting point, not proof of resilience. Follow up testing findings, address root causes and make it safe for staff to raise risks.
- Include critical suppliers in exercises and establish testing and access expectations in contracts. Map supplier concentration and plan for a provider becoming unavailable.
- Operational technology can be difficult to patch without affecting safety or support. Agree practical controls with providers and design for continued service during disruption.
Government’s Supply Chain Problem Is Becoming a National Security Problem
Amelia Edge — Australian Women in Security Network
- Government services depend on layers of suppliers, including small businesses with limited security resources. Map those dependencies beyond the first contracted provider.
- Help suppliers build practical capability, not just awareness. Edge described a programme connecting students and graduates with small businesses to work on real security projects.
- Treat procurement as a resilience decision. Bring procurement, cyber, risk and executive teams together to test what happens if a critical supplier fails.
Cyber Without Borders: Strengthening International Partnerships for Collective Resilience
Lance Domm — British High Commission
- Cyber threats cross borders, so national resilience depends on international information sharing, capacity building and coordinated action.
- The United Kingdom’s approach pairs an open digital environment with security, international law and responsible state behaviour. These principles provide a basis for cooperation with Australia.
- Commercial intrusion tools and ransomware require different partners to work together. Diplomacy, operational disruption, attribution and sanctions are complementary tools, not standalone solutions.
AI Is Creating a Government Australia Has Never Operated Before
Craig Bickell — Department of Home Affairs
The Hon. Victor Dominello — Future Government Institute
- Apply existing governance and security disciplines to AI, strengthening them where the technology changes the risk. Controls should be proportionate to the consequences of each use.
- Citizen-facing services need to consider both human users and AI agents. Identity, transparency and trust matter as agencies explore more connected service delivery.
Help your peers
Share what you've learned with fellow public servants